News
 News
MariaDB Foundation: Ecosystem Hub Surpasses 200 Listed Solutions
MariaDB Foundation's open source directory reaches 200 entries six months after launch: hosting, backup, monitoring, migration and more.
 News
USN-8896-1: GStreamer Ugly Plugins flaws, risk of code execution
Ubuntu reports vulnerabilities in GStreamer Ugly Plugins related to malformed RealMedia and ASF files: potential arbitrary code execution.
 News
USN-8900-1: Go Networking flaws risk denial of service via HTTP/2
Ubuntu reports two vulnerabilities in the Go Networking package that can cause denial of service on HTTP/2 connections.
 News
Let's Encrypt: 64-day certificates by default from 10 February 2027
From 10 February 2027, Let's Encrypt will issue 64-day certificates by default. Staging tests start 14 October 2026; the last 90-day certificate expires on 11 May 2027.
 News
USN-8891-1: librsvg flaw risks crashes or code execution
Ubuntu fixes a librsvg flaw (CVE-2026-96889) that opens the door to crashes or code execution via malicious SVG files. Updates for 24.04 and 26.04 LTS.
 News
LSN-0122-1: live patch for dozens of use-after-free flaws in the Ubuntu kernel
Canonical releases live patch LSN-0122-1, fixing dozens of use-after-free and DoS bugs in the Linux kernel across all supported Ubuntu releases, with no reboot required.
 News
USN-8894-1: poppler flaws, update on Ubuntu 22.04, 24.04 and 26.04 LTS
Five vulnerabilities in poppler, the PDF rendering library, can cause crashes or code execution. Ubuntu has released patches for 22.04, 24.04 and 26.04 LTS.
 News
USN-8895-1: sudo flaw bypasses NOTBEFORE/NOTAFTER time restrictions
A bug in sudo lets a local user bypass sudoers time restrictions by manipulating the TZ variable. Patches available for 22.04, 24.04 and 26.04 LTS.
 News
Cloudflare Managed Defense: a multi-agent harness to filter security alerts
Cloudflare has put into beta a multi-agent system that separates evidence gathering from AI analysis to cut false positives on Managed Defense.
 News
Grafana Cloud Synthetic Monitoring: folders for checks reach GA
Grafana Cloud has brought folders for organising Synthetic Monitoring checks to general availability, complete with permissions, API support and Terraform integration.
 News
DNS root KSK rollover on 11 October 2026: what to check on your resolvers
On 11 October 2026 the DNS root changes its DNSSEC key-signing key. Anyone running a validating resolver must verify that the new trust anchor (key tag 38696) is active.
 News
USN-8893-1: two libwebsockets flaws, risk of remote code execution
Ubuntu has published security advisory USN-8893-1: two vulnerabilities in libwebsockets allow crashes or remote code execution.
 News
Laravel 13 natively supports MariaDB Vector, no external packages needed
From Laravel 13.28, vector columns and similarity queries work on MariaDB 11.7+ without external packages or pgvector.
 News
USN-8890-1: eight libsoup flaws, from DoS to possible code execution
Ubuntu publishes USN-8890-1: eight CVEs in libsoup2.4 and libsoup3, ranging from denial of service to possible code execution via HTTP/2.
 News
USN-8892-1: Ubuntu Pro for WSL Exposes the Activation Token
A bug in wsl-pro-service exposes the Ubuntu Pro token in command-line arguments. A fix is available for all supported releases.
 News
USN-8884-1: four U-Boot flaws, risk of code execution
Ubuntu fixes four vulnerabilities in U-Boot that could lead to code execution or denial of service on embedded systems.
 News
USN-8883-1: Go flaw allows bypass of hostname checks via Punycode
Ubuntu fixes a flaw in Go's x/net/idna package that could allow bypassing hostname-based access controls.
 News
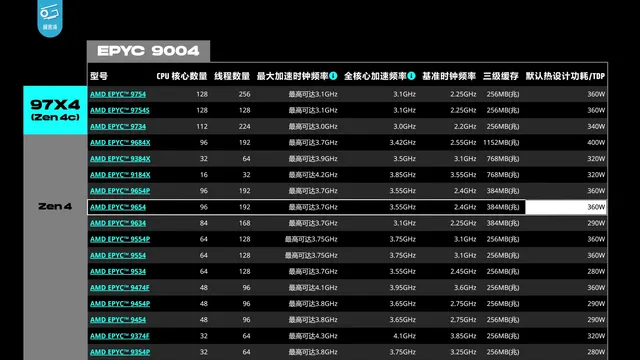
USN-8887-1: Linux kernel flaws, one compromising SEV-SNP guest integrity
Ubuntu has published USN-8887-1: multiple Linux kernel flaws, including one affecting AMD processors that puts the memory integrity of SEV-SNP guests at risk.
 News
USN-8885-1: two FluidSynth flaws fixed via Ubuntu Pro ESM Apps
Ubuntu has flagged two vulnerabilities in FluidSynth that can cause crashes or arbitrary code execution. A patch is available via Ubuntu Pro ESM Apps.
 News
USN-8874-1: sg3-utils flaw risks arbitrary command execution as root
Ubuntu patches CVE-2026-16313 in sg3-utils: unsanitised device identification data could lead to arbitrary command execution.